Qt / C++ infos
-
Security advisory: CVE-2026-95620 Use-after-free vulnerability in QNetworkAccessManager HTTP/2 support impacts Qt
A use-after-free vulnerability in the Qt QNetworkAccessManager HTTP/2 client support of the Qt Network module has been discovered and has been assigned the CVE id CVE-2026-95620.
-
Security advisory: CVE-2026-16762 Denial-of-service vulnerability in the Qt Core QXmlStream parser (QXmlStreamReader) impacts Qt
A denial-of-service vulnerability in the Qt Core QXmlStream parser (QXmlStreamReader) of the qtbase component has been discovered and has been assigned the CVE id CVE-2026-16762.
-
Security advisory: CVE-2026-96432 - Null pointer dereference vulnerability in QNetworkAccessManager impacts Qt
A null pointer dereference vulnerability in the Qt QNetworkAccessManager class of the Qt Network module has been discovered and has been assigned the CVE id CVE-2026-96432.
-
Security advisory: CVE-2026-105923 - Null-pointer dereference in QTriangulator reachable through VectorImage
A denial-of-service vulnerability in the Qt Framework VectorImage QML type of the Qt Quick Vector Image module has been discovered and has been assigned the CVE id CVE-2026-105923.
Affected versions: from Qt 6.8.0 to Qt 6.8.8, from Qt 6.9.0 to Qt 6.11.2
Impact: Processing specially crafted SVG content with the VectorImage QML type can cause the application to crash, resulting in loss of availability.
CVSS 4.0 Score: 4.0 / MEDIUM
Vector String: CVSS:4.0/AV:L/AC:L/AT:N/PR:N/UI:A/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N/E:U/AU:N/R:U/RE:L/U:Green
Mitigation: Do not load untrusted SVG files with the VectorImage QML type.
Solution: Apply the following patch or update to Qt 6.8.9, Qt 6.11.3 or Qt 6.12.0 or later.
Patches:
dev: https://codereview.qt-project.org/c/qt%2Fqtbase/+/762279 -
Updated Qt Code Review Skills Reduce Token Costs by Up To 75%
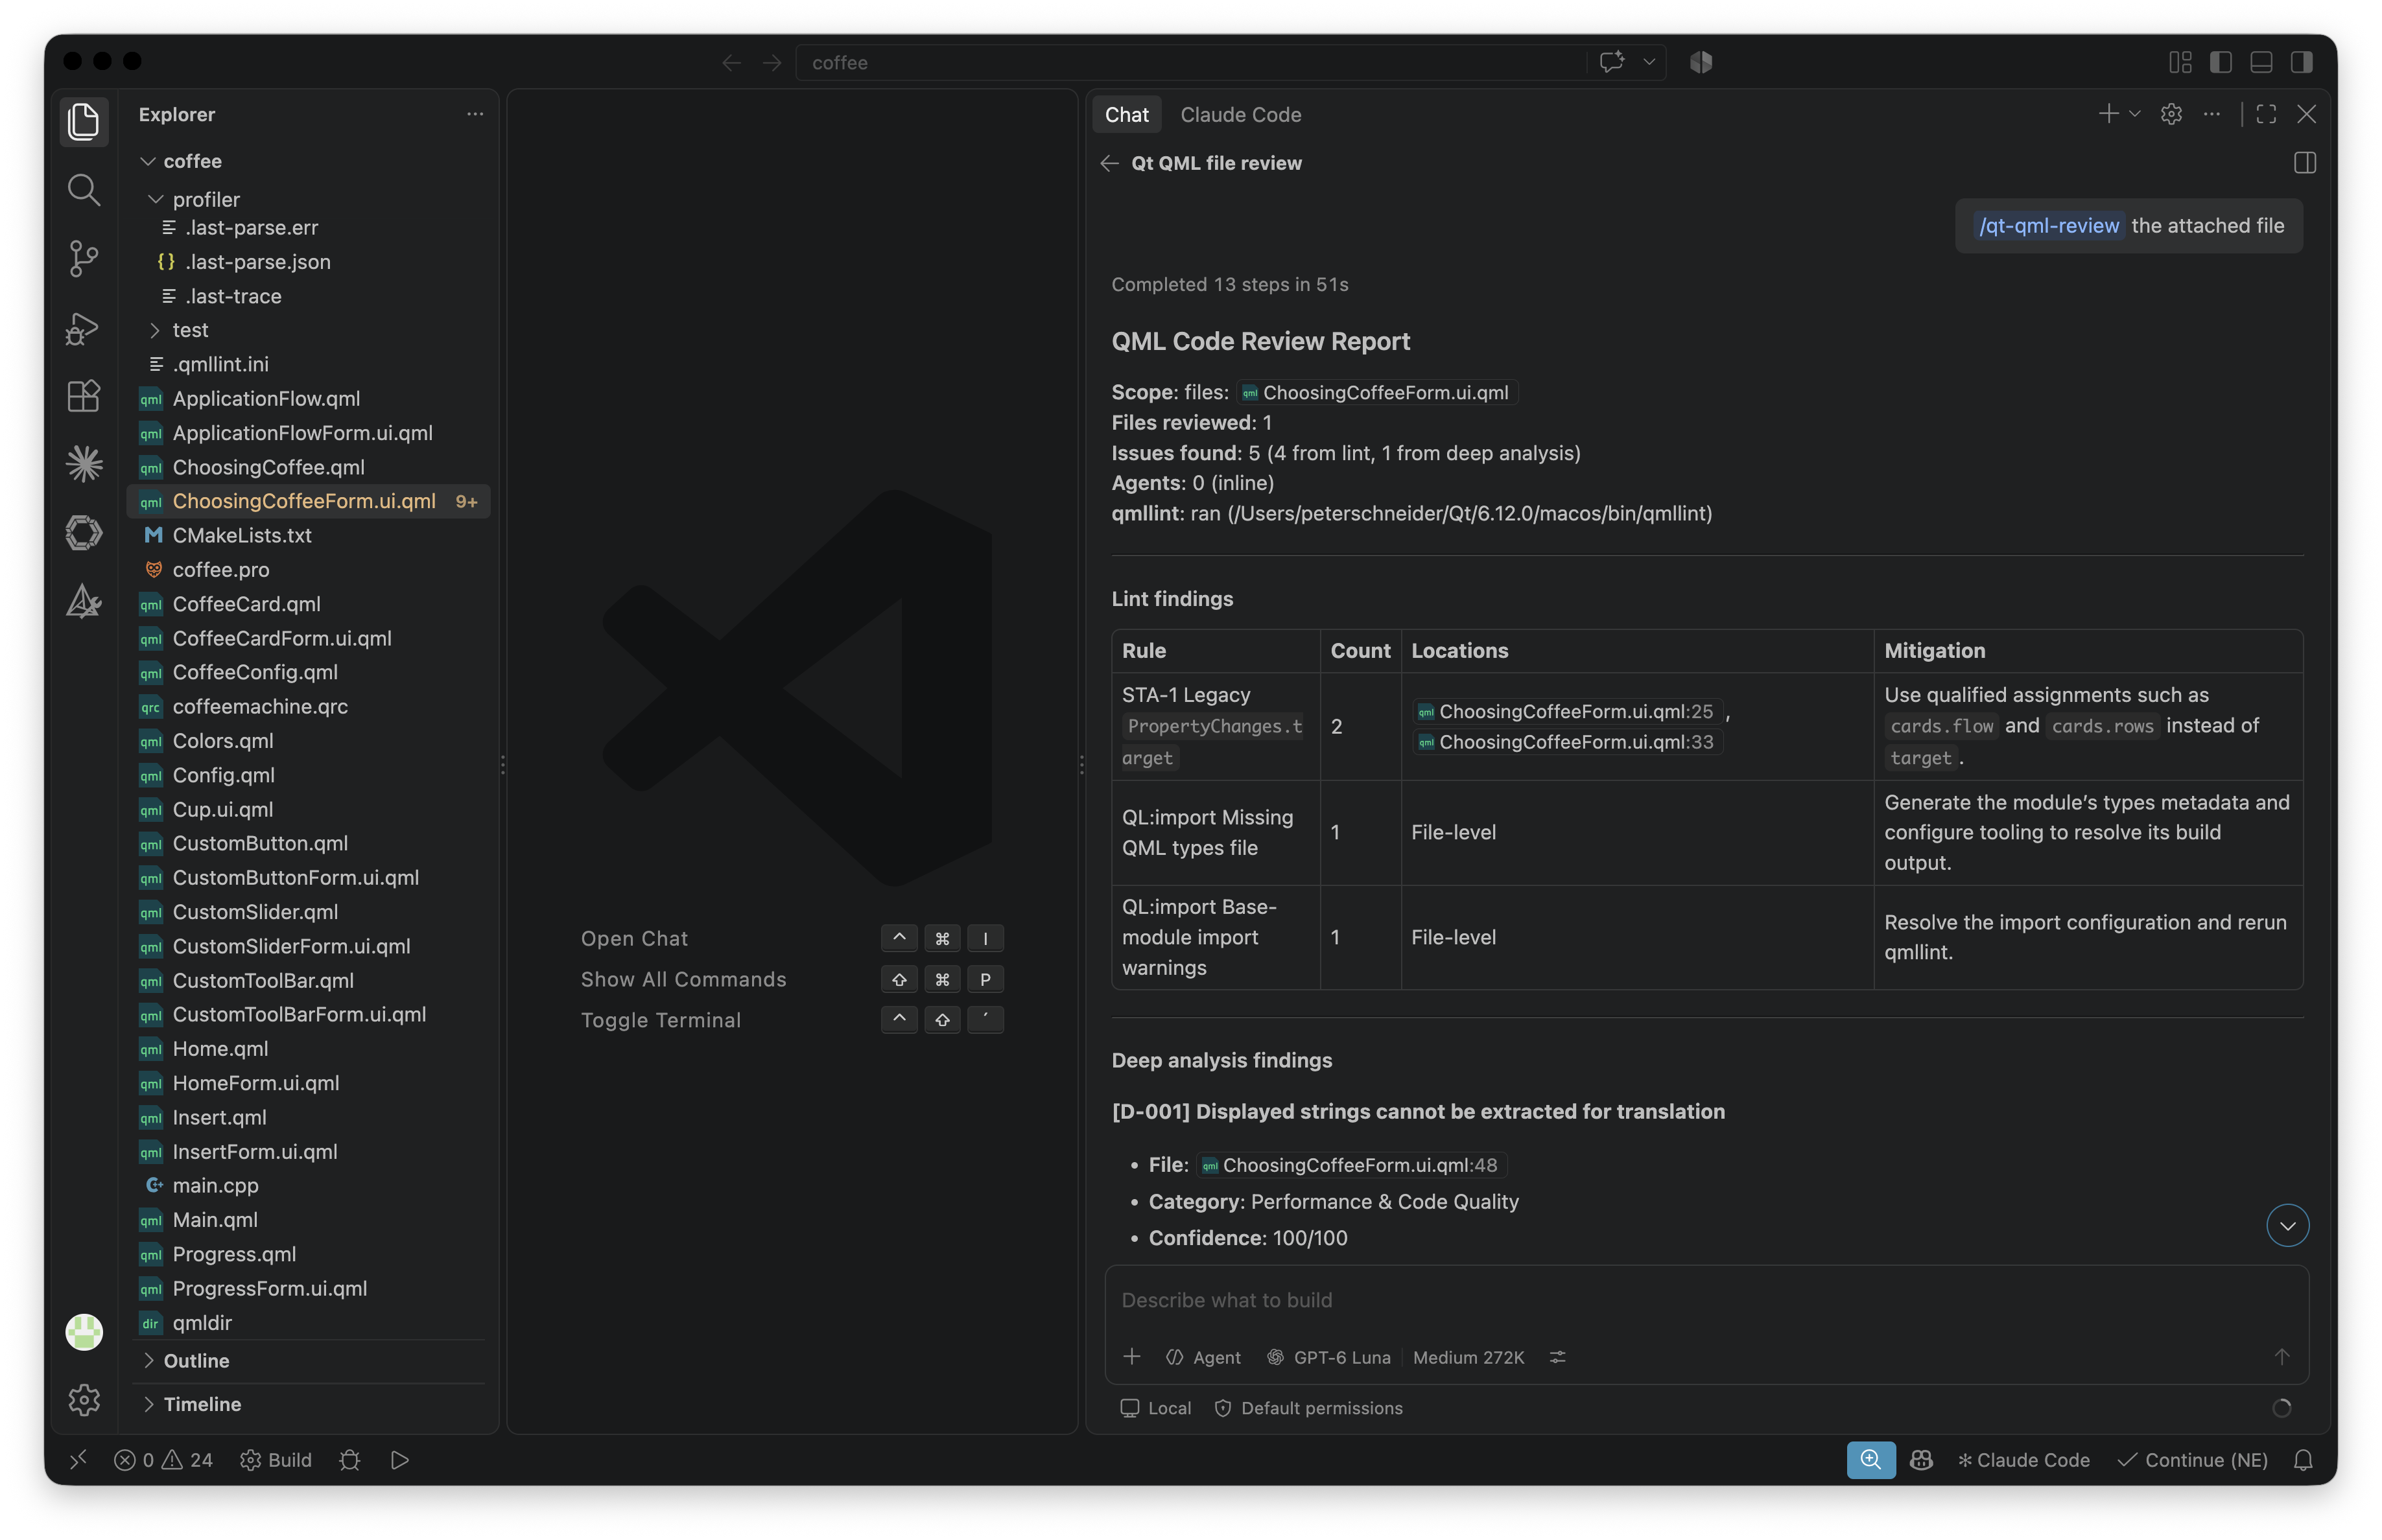
Whether you are reviewing Qt Quick or Qt Widget code with Qt’s agentic skills, you can reduce your token consumption significantly by upgrading to the latest versions while getting the same review quality.
-
Security advisory: CVE-2026-101201 Out-of-bounds read vulnerability in JSON document parsing functionality impacts Qt Core and Qt 5 Core Compatibility APIs
An out-of-bounds read vulnerability in the JSON document parsing functionality (QJsonDocument) of the Qt Core module and the Qt 5 Core Compatibility APIs module (QBinaryJson) has been discovered and has been assigned the CVE id CVE-2026-101201.
-
Qt Creator 21 - CMake Changes
Here are the new CMake changes in Qt Creator 21:
-
Security advisory: CVE-2026-8168 Denial-of-service vulnerability in the SVG parser and renderer impacts Qt
A denial-of-service vulnerability in the parser and renderer of the Qt SVG module (QtSvg) has been discovered and has been assigned the CVE id CVE-2026-8168.
-
Qt Creator 21 Beta2 released
We are happy to announce the release of Qt Creator 21 Beta2.
-
Qt for Python Release: 6.12 is here!

Qt for Python 6.12 is here, alongside the Qt 6.12 LTS release. This is the biggest release we have had in a while. If you haven't read what's new in Qt itself,check out the general announcement.